Access (API Tokens and OAuth)
The Access tab controls what can read and manage your workspace's data besides a person signed in to the app: AI assistants, MCP clients and scripts. The SparkLogs Agent does not use this tab. Agents enroll with registration tokens.
Open Workspace Settings in the sidebar, then Access.
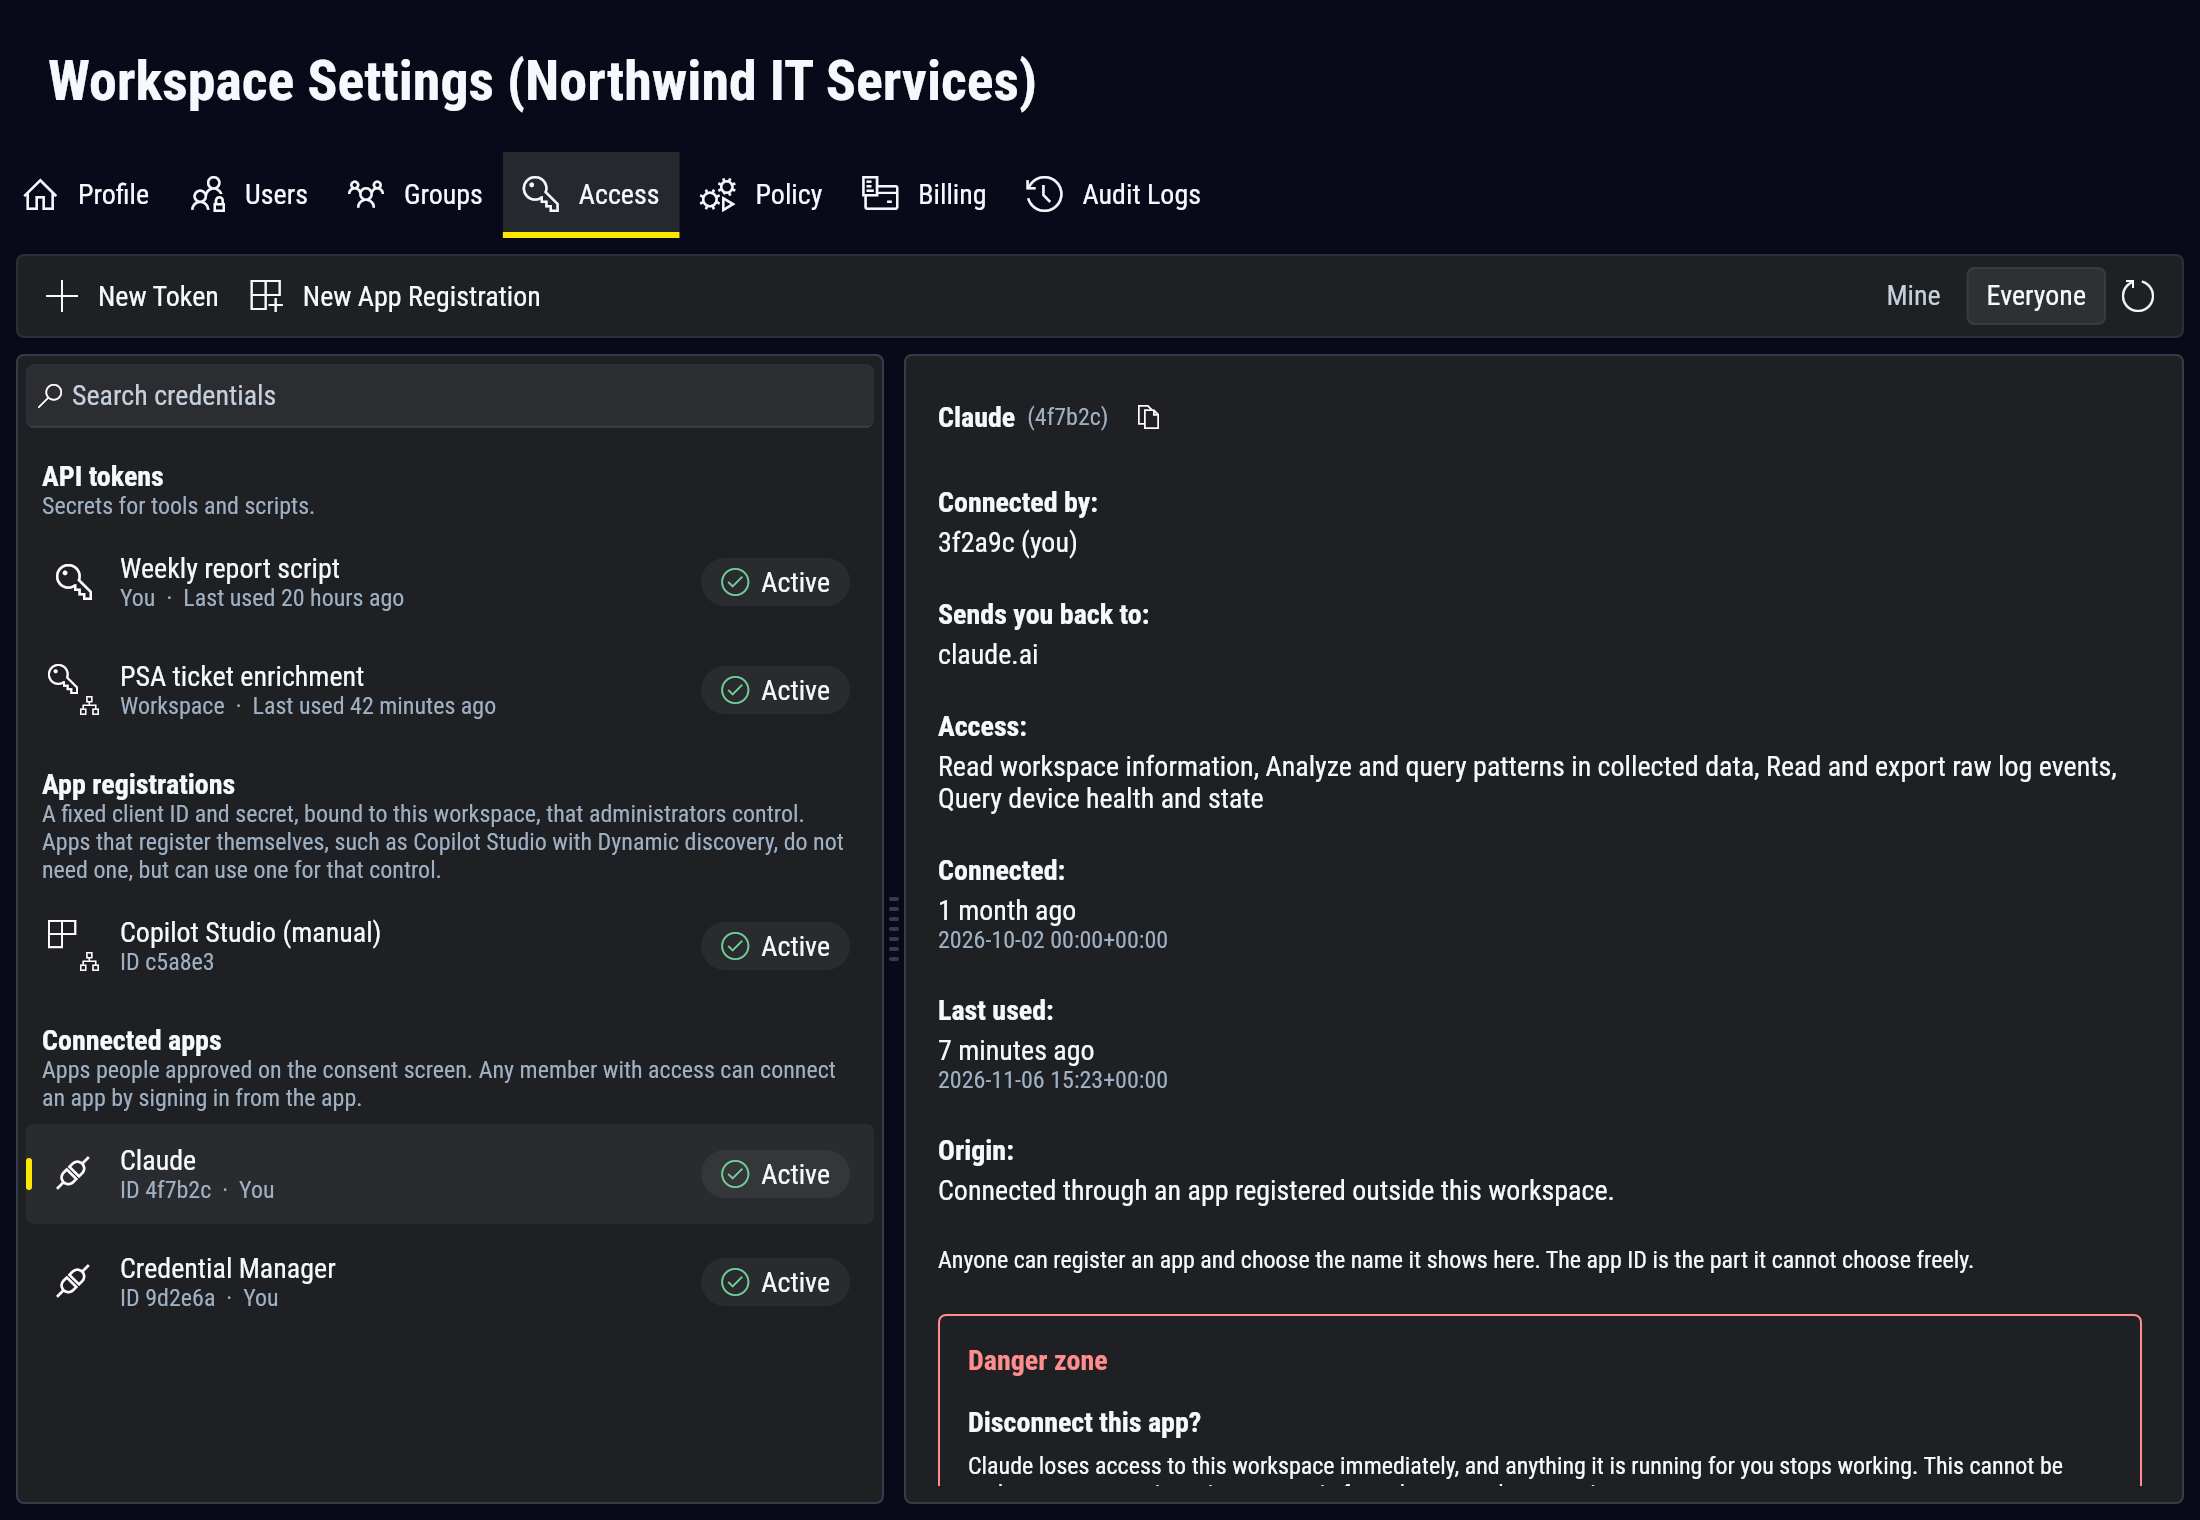
The list on the left has three sections:
| List | What it holds | Who needs it |
|---|---|---|
| Connected apps | AI apps that someone approved by signing in. | Anyone who connects an AI assistant. |
| App registrations | A client ID and secret that an Administrator created for one app. | Administrators, for an app that cannot register itself. |
| API tokens | Secrets for hosts that cannot sign in. | Anyone building a programmatic integration or an automation. |
Connected apps
When you connect an AI assistant, it opens the SparkLogs consent screen in your browser. You pick the workspace, the scopes the app may use, and the organizations it may reach.
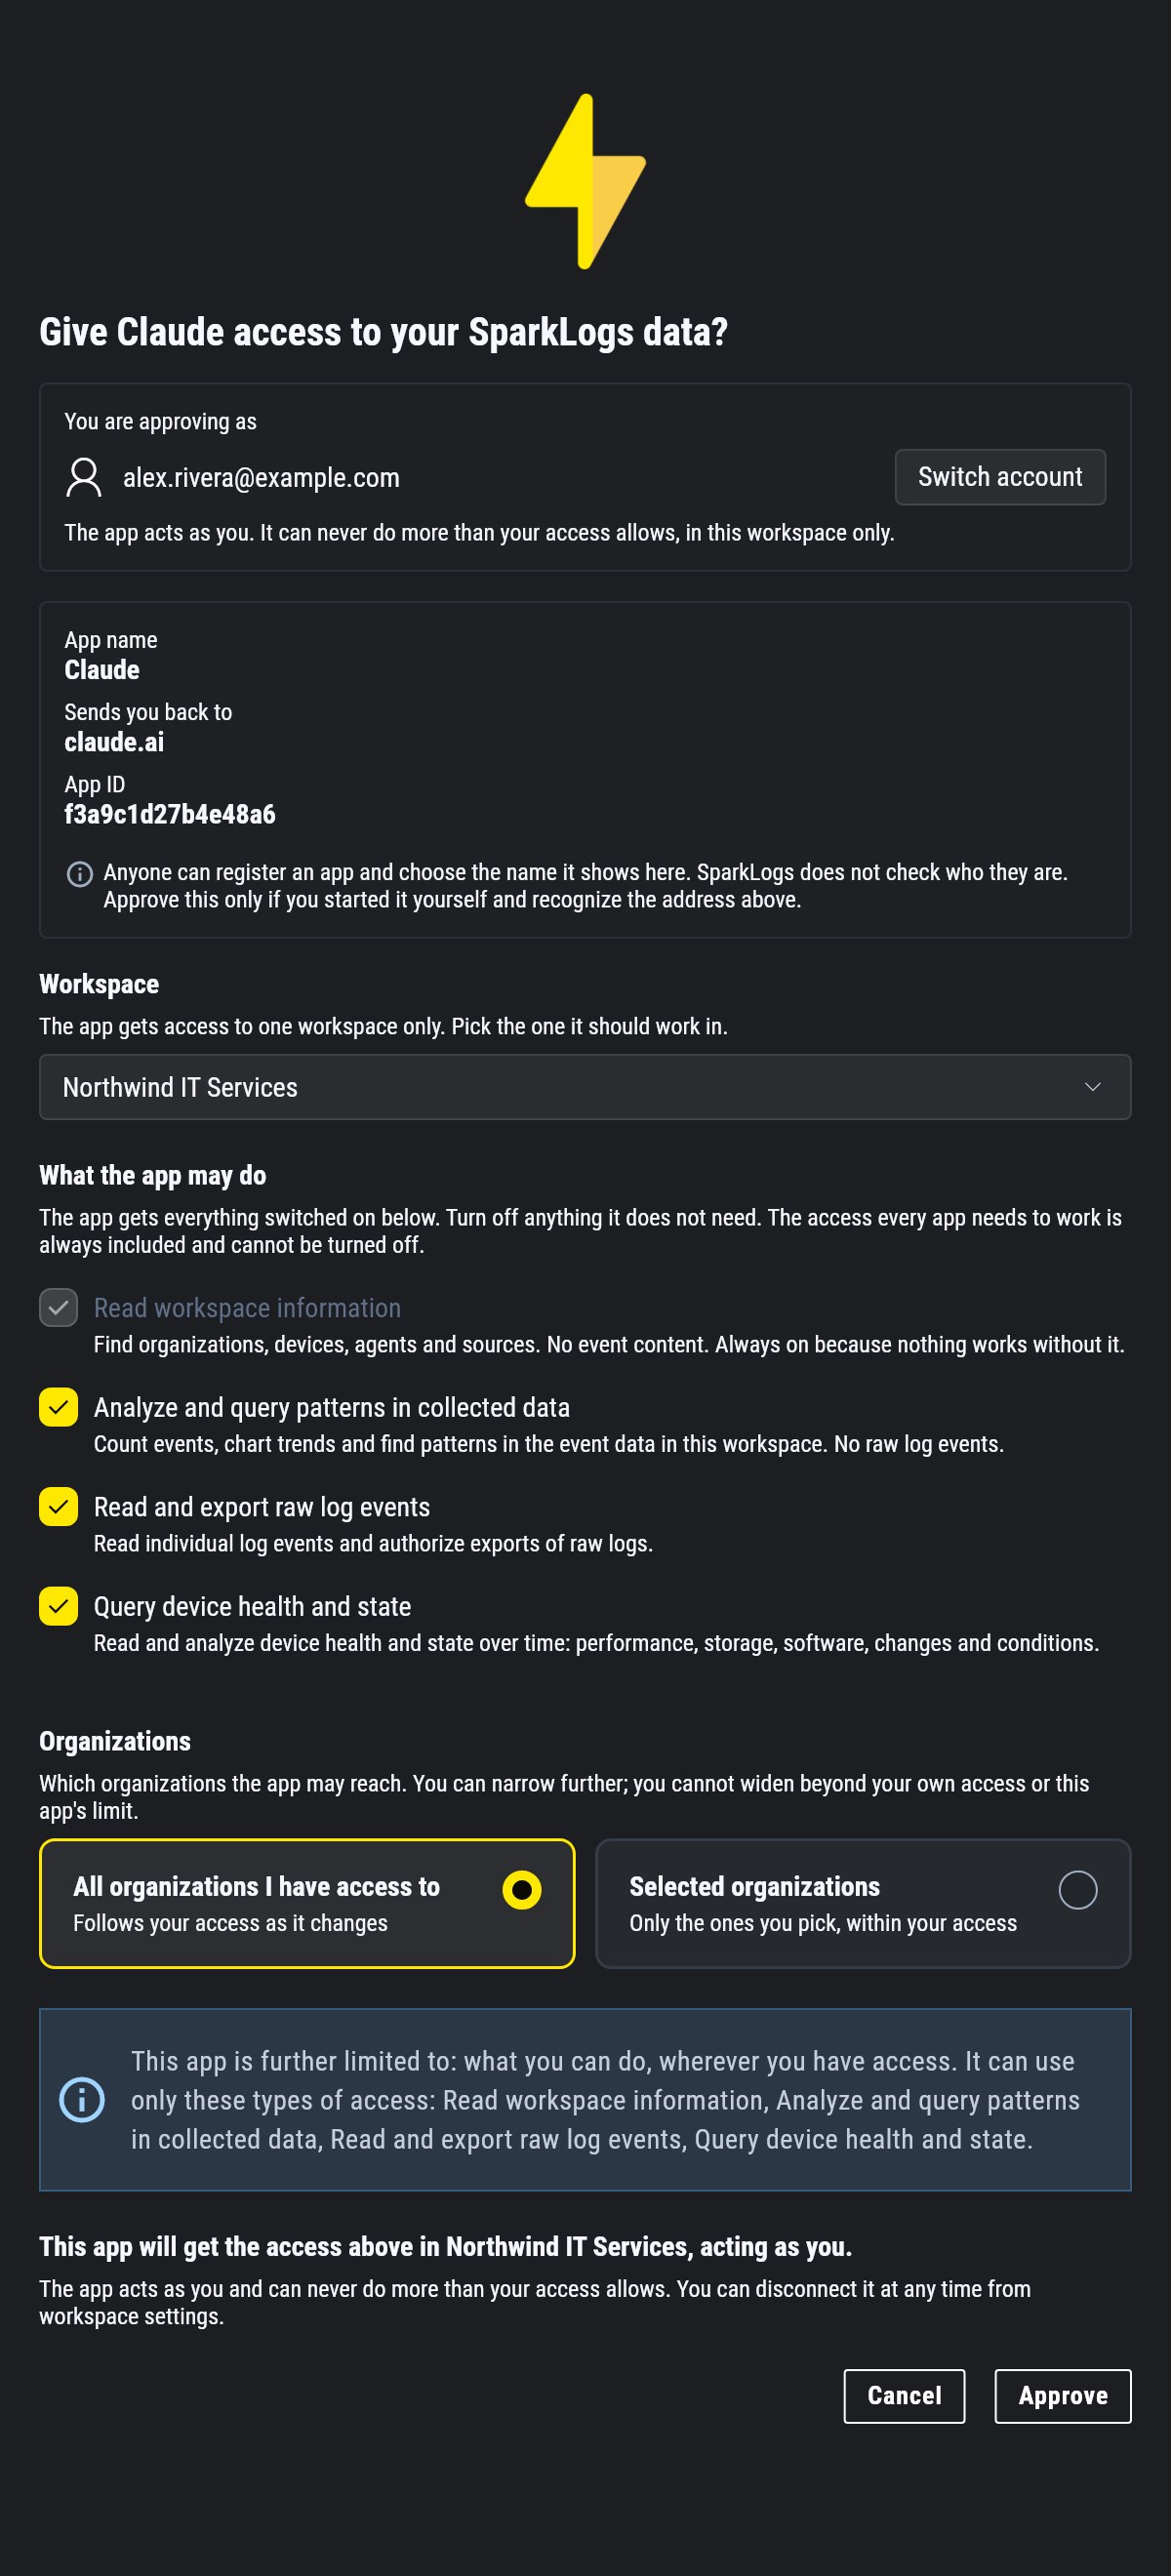
After you approve, the app appears under Connected apps. It acts as you, so it can do no more than your own access allows, and the scopes you approve narrow that further. Anyone who has access in the workspace can approve an app. To revoke an app's access, select it and choose Disconnect.
| Scope | Shown as | What it allows |
|---|---|---|
workspace:read | Read workspace information | Find organizations, devices, agents and sources. Always included. |
events:query | Analyze and query patterns in collected data | Count events, chart trends and find patterns. No raw log events. |
events:read | Read and export raw log events | Read individual log events and authorize exports of raw logs. |
devices:read | Query device health and state | Read and analyze device health and state over time. |
analytics:read | Query App Analytics | Run queries over App Analytics. Offered only when the workspace has App Analytics and your role includes it. |
The consent screen offers only the scopes your access can use. If you gain access later, reconnect the app to add the matching scope.
App registrations
Most AI apps register themselves when they connect and need no setup here. That includes Claude, Cursor, Codex, and Copilot Studio with Dynamic discovery.
Create an app registration when a platform cannot register itself, or when you want to hold the client ID and secret yourself, as with Copilot Studio's Manual OAuth type. Only an Administrator can create one. It is a fixed client ID and secret, bound to this workspace.
Select a registration to see its notes, return addresses, the access it may ask for and the organizations it may reach. Change any of them with Edit Registration on the command bar, or with the pencil beside the field. The + on Secrets adds a secret and keeps the previous one working for 21 days, which gives you time to update the platform.
API tokens
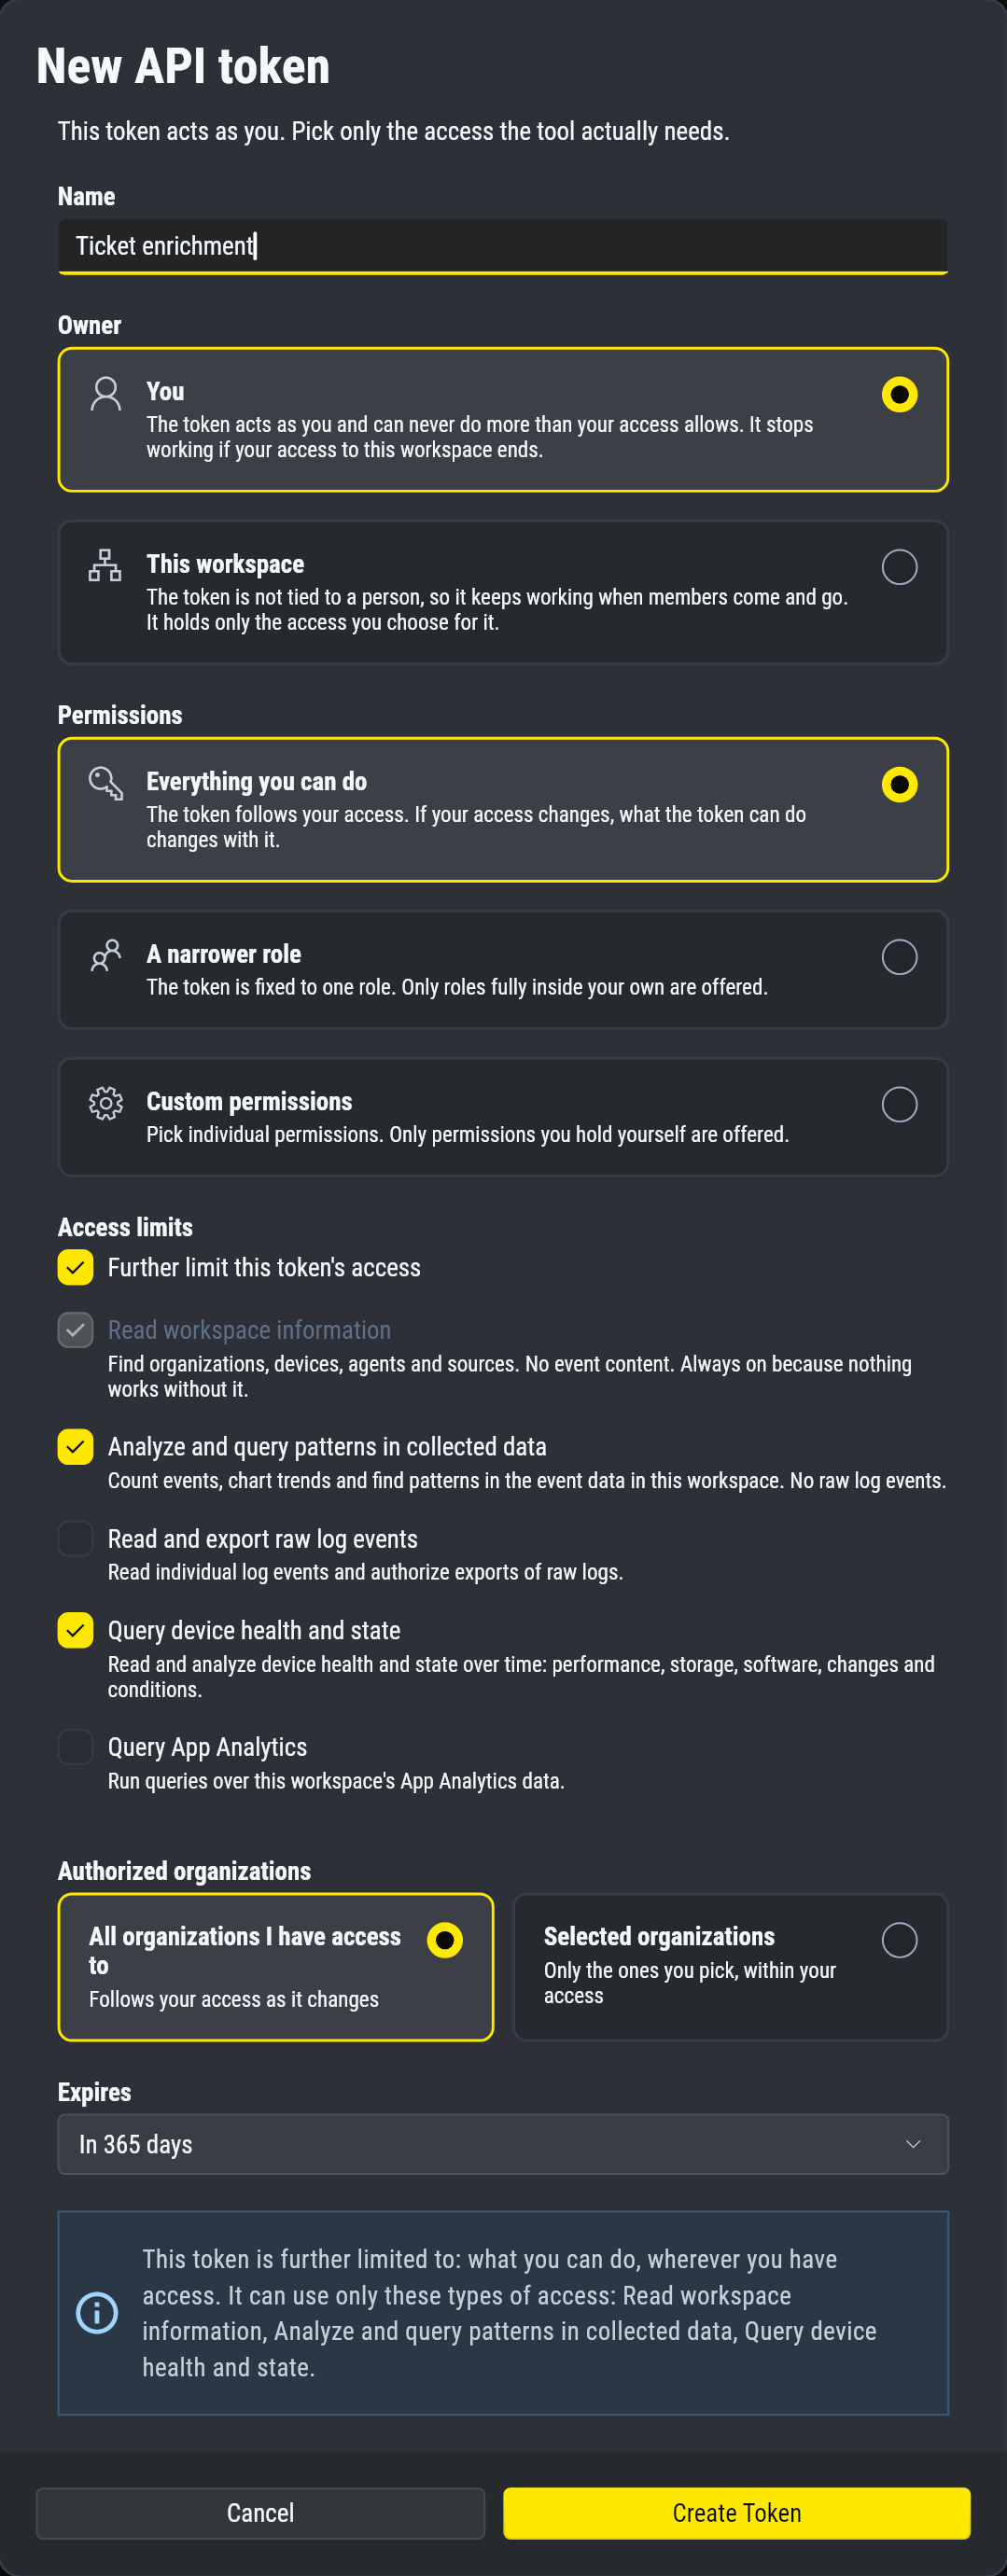
Use an API token for a programmatic integration or an automation whose host cannot sign in with OAuth, such as a scheduled job that accepts only a static secret. There are two kinds.
| Personal token | Workspace token | |
|---|---|---|
| Who can create it | Anyone with access, for themselves. | Administrators and Organization Administrators. |
| What it can do | What you can do. You can fix it to a narrower role, chosen permissions or chosen organizations. | What its own access grants allow: a role and where it applies. That can be no more than your access when you create it. |
| When its creator leaves the workspace | It is revoked. | It keeps working. |
When you create either kind, Further limit this token's access fixes the token to the scopes you pick. Left off, the token can use every scope its access allows.
Use a token
The app shows the secret once, when you create the token. Treat it like a password and keep it in your host's secret store.
Send it as a bearer token on each request:
Authorization: Bearer <token>
Where that header goes depends on the host. For the MCP server, see Connect.
Change, rotate or revoke a token
Select a token to see its owner, what it may do, its access limits, when it expires and when it was last used. Access limits lists the scopes the token is fixed to by name, or says No limits.
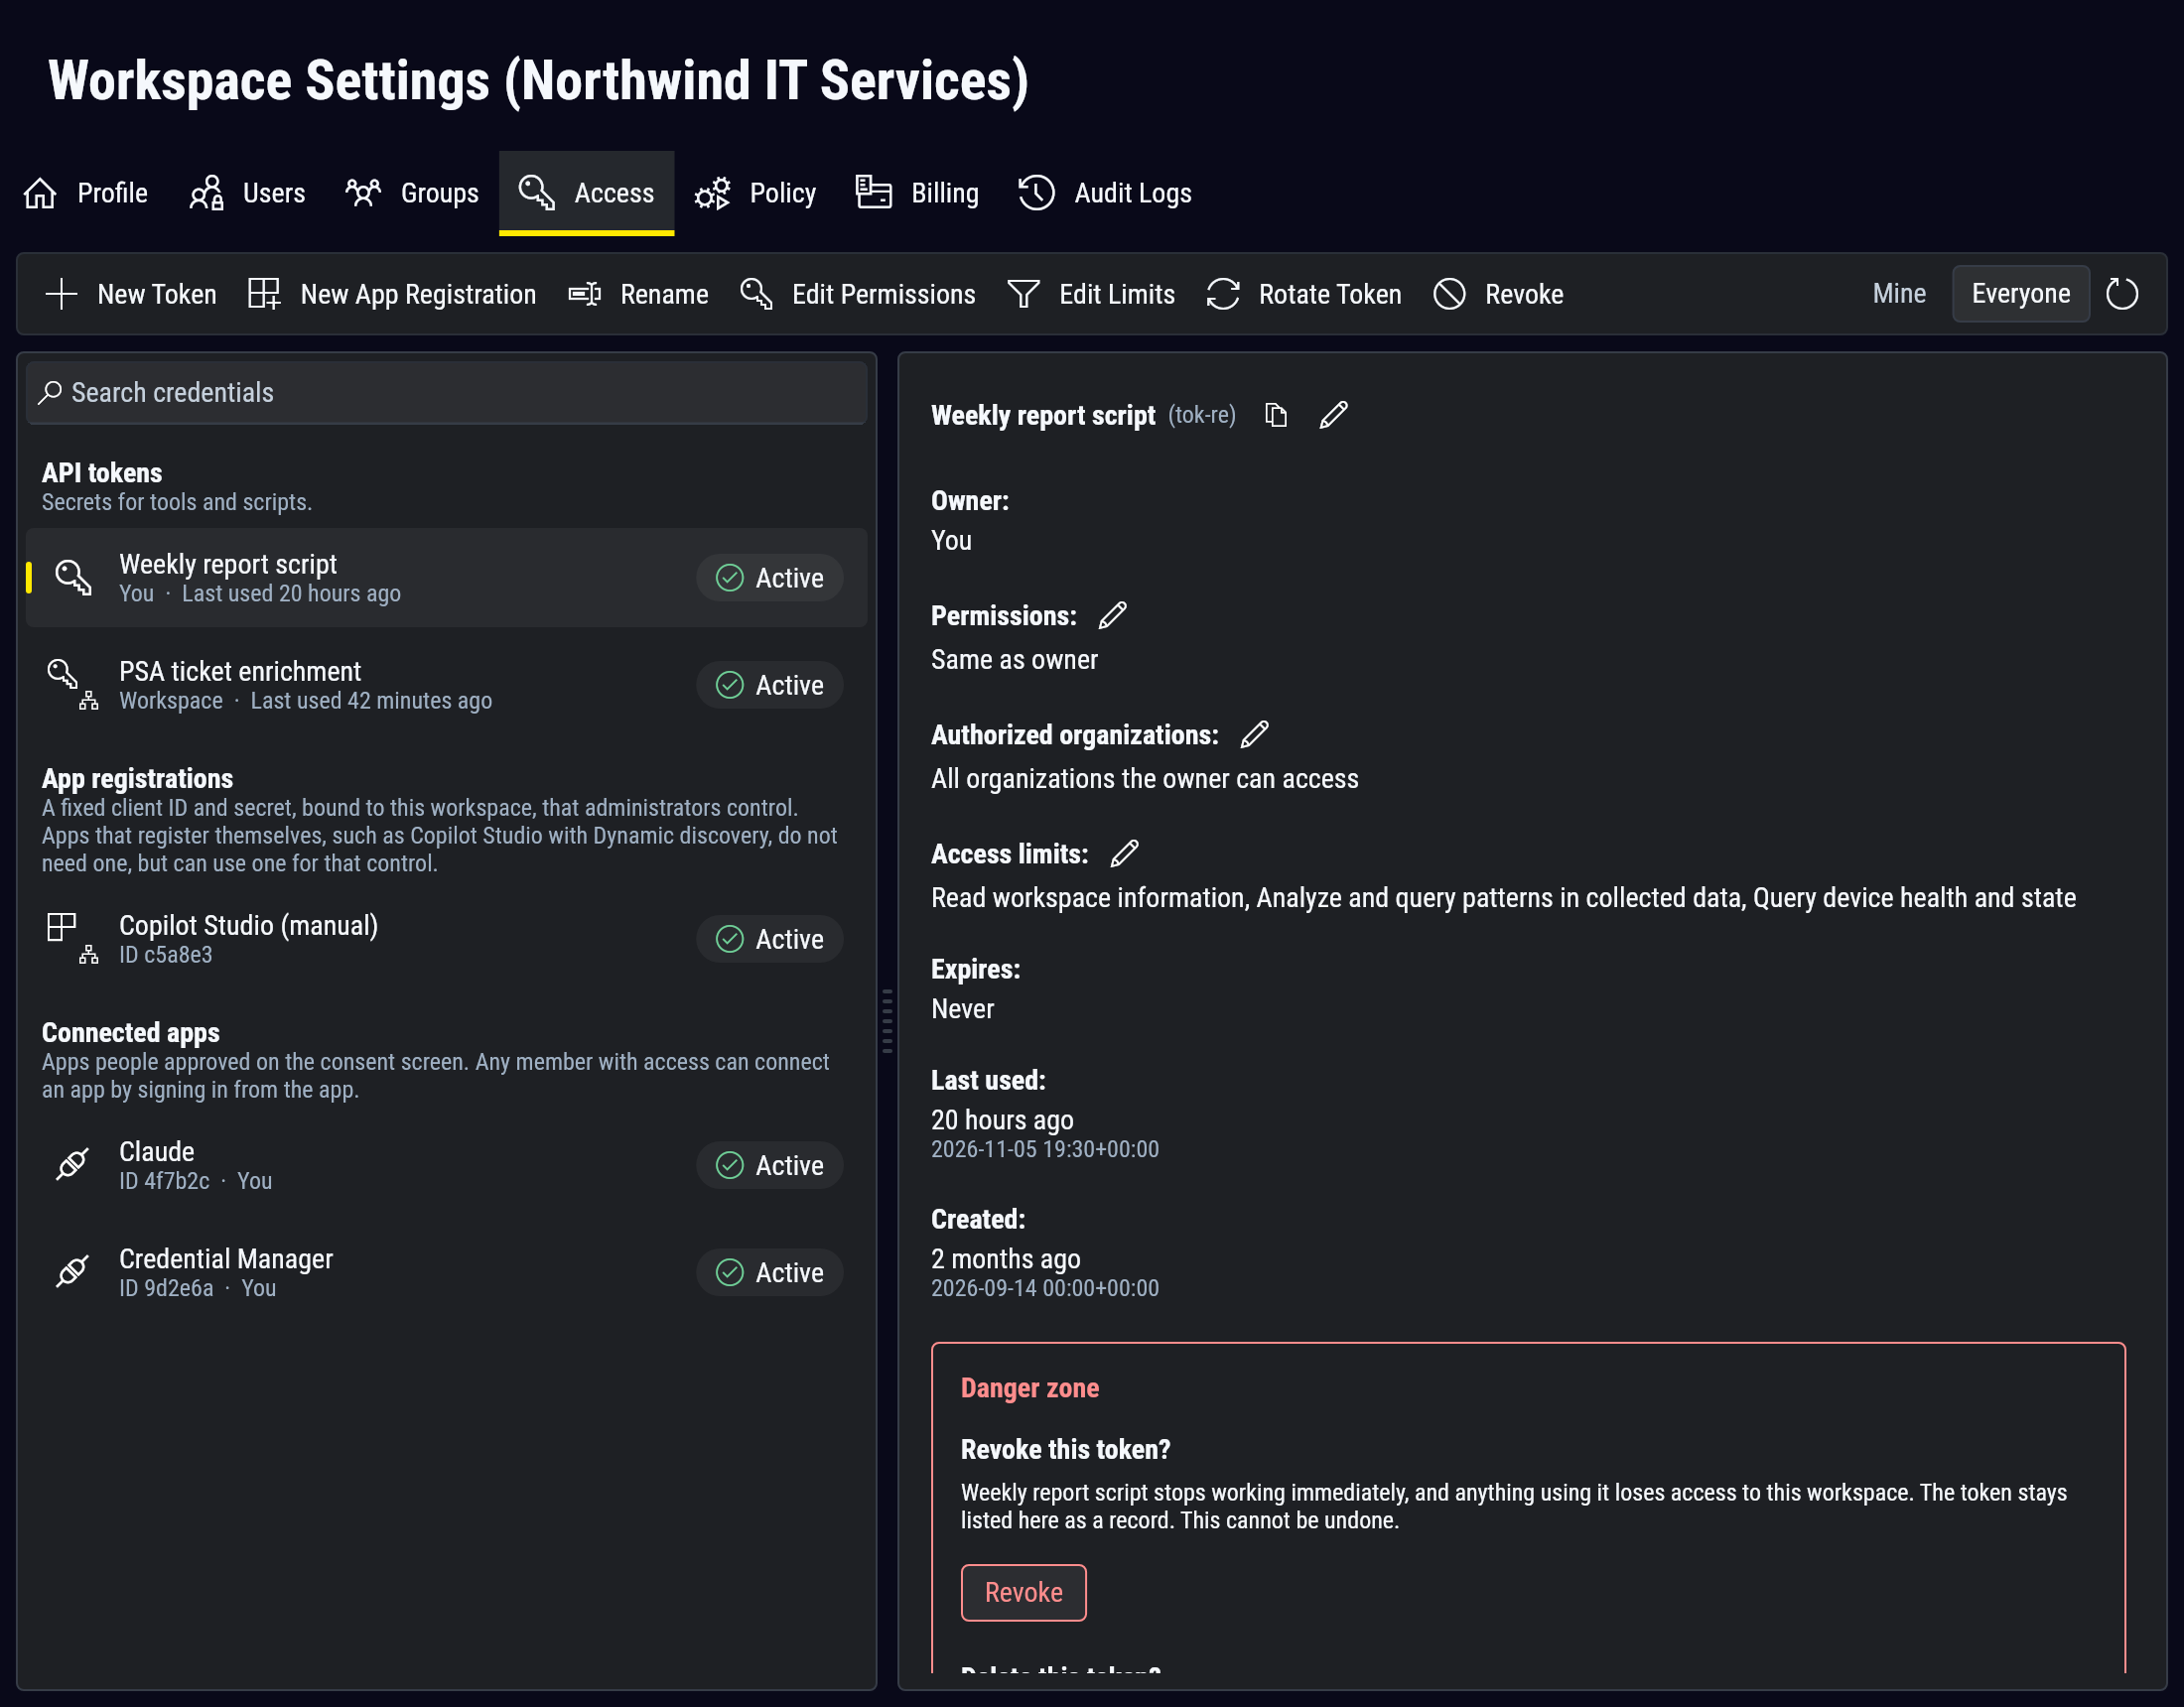
The command bar acts on the selected token, and the pencil beside a field opens the same editor.
| Action | What it does |
|---|---|
| Rename | Changes the token's name. |
| Edit Permissions | On a personal token, changes what it may do and in which organizations. |
| Edit Access | On a workspace token, changes its access grants. |
| Edit Limits | Changes which scopes it may use. |
| Rotate Token | Replaces the secret. The old secret stops working at once. |
| Revoke | Stops the token at once and keeps it listed as a record. You cannot undo it, so create a new token if you still need access. |
| Delete | Stops the token and removes it from the list. |
Revoke and Delete are in the danger zone on the token's details. A button you cannot use says why when you point at it.
Who sees which tokens and apps
The lists always show your own tokens and connected apps. Administrators, Organization Administrators and Auditors also see other people's tokens and apps, and workspace tokens, when that access is given on their organizations or below them.
You can manage another person's token or app, or a workspace token, only when your own access includes all of its access. One that also covers organizations you can't see is read-only for you. The rule is the same as for people and groups, described in Who you can see.